Six Sigma Risk Management: FMEA, RPN and Control Plans
Yes, Six Sigma is a sound way to manage risk, because it turns a vague worry into a number you can rank, reduce and re-measure. The core tool is failure mode and effects analysis (FMEA), which scores each way a process can fail on severity, occurrence and detection and multiplies the three into a risk priority number (RPN). DMAIC then drives that number down and a control plan keeps it there.
How does Six Sigma manage risk instead of just listing it?
A conventional risk register records what might go wrong and gives each item a colour. Six Sigma asks a harder question: how often does this process already fail, how much would a failure cost, and would we notice before the customer did? Those three questions are measurable, so the answer is a figure rather than an opinion.
Two ideas carry most of the weight. The first is that risk and variation are close relatives: a process that wanders far from its target eventually produces a defect, and a defect is a risk that has happened. The second is that you can express the failure rate as defects per million opportunities (DPMO) and compare very different processes on one scale.
| Sigma level | Defects per million opportunities | What it means for risk |
|---|---|---|
| 3 | 66,807 | Roughly one failure in every fifteen opportunities |
| 4 | 6,210 | Failures are rare but still visible every week |
| 5 | 233 | A failure is a surprise worth investigating |
| 6 | 3.4 | Failures are close to unheard of |
These figures use the conventional 1.5-sigma shift that Six Sigma practitioners apply to long-term performance. The Wikipedia article on FMEA gives a neutral summary of the scoring method itself.
Enterprise risk frameworks such as ISO 31000 tell an organisation to identify, analyse, evaluate and treat risk. Six Sigma does not replace that cycle. It supplies the data-driven tools for the analysis and treatment steps, which is where most frameworks stay vague.
Where does risk appetite fit?
Leadership still decides how much risk the organisation accepts. Six Sigma contributes by linking objectives to the voice of the customer, the voice of the business and the voice of the regulator, so the tolerance for failure comes from stated requirements rather than from habit. A requirement such as "no invoice leaves with the wrong tax code" can be measured, which a general intention to be careful cannot.
How does an FMEA score a risk?
An FMEA starts with a process map or a product design and walks through it step by step. For each step the team lists the ways it could fail (the failure mode), what happens downstream if it does (the effect), and why it might happen (the cause). Each failure mode then gets three scores, usually on a 1 to 10 scale.
- Severity (S): how bad the effect is for the customer or the business. A 10 is a safety or legal consequence; a 1 is something nobody would notice.
- Occurrence (O): how likely the cause is to arise. A 10 means it is almost certain; a 1 means it is remote.
- Detection (D): how likely the current controls are to catch the failure before it reaches the customer. The scale runs the opposite way, so a 10 means the failure would almost certainly escape.
Multiply the three and you have the RPN, a number from 1 to 1,000. Because detection is built into the score, an FMEA can distinguish between a failure that is frequent but always caught at inspection and one that is rare but invisible until a customer complains.
Which version of FMEA do you use?
A design FMEA (DFMEA) examines a product or service design for weaknesses before it is released. A process FMEA (PFMEA) examines how the work is carried out, which is the usual choice inside a DMAIC project. Many teams also keep a separate FMEA for a supplier process they depend on, since a supplier failure is still your failure in the customer's eyes.
What are the limits of the RPN?
The RPN is useful and easy to criticise at the same time. Different combinations give the same product: a failure scoring 9, 2 and 5 and another scoring 3, 5 and 6 both come to 90, yet the first is far more serious. The scales are also ordinal, so doubling an RPN does not double the risk. Many teams therefore apply a rule on top of the arithmetic: any failure mode with a severity of 9 or 10 gets an action plan whatever its RPN.
The automotive industry went further. The AIAG and VDA FMEA Handbook published in 2019 replaced the RPN ranking with an Action Priority table that sorts combinations of severity, occurrence and detection into High, Medium and Low. Outside the automotive supply chain the classic RPN is still the norm, and it is the version the ASQ Black Belt exam asks about.
Which failure modes should you fix first?
Take an order-to-cash process at a distributor that ships to business customers. The team maps it, lists the failure modes and scores them. The table shows four of the rows, ranked by RPN.
| Failure mode | S | O | D | RPN |
|---|---|---|---|---|
| Wrong price loaded for a contract customer | 7 | 5 | 6 | 210 |
| Credit check skipped on a large order | 9 | 3 | 7 | 189 |
| Delivery address does not match the order | 6 | 6 | 4 | 144 |
| Duplicate invoice raised | 5 | 4 | 3 | 60 |
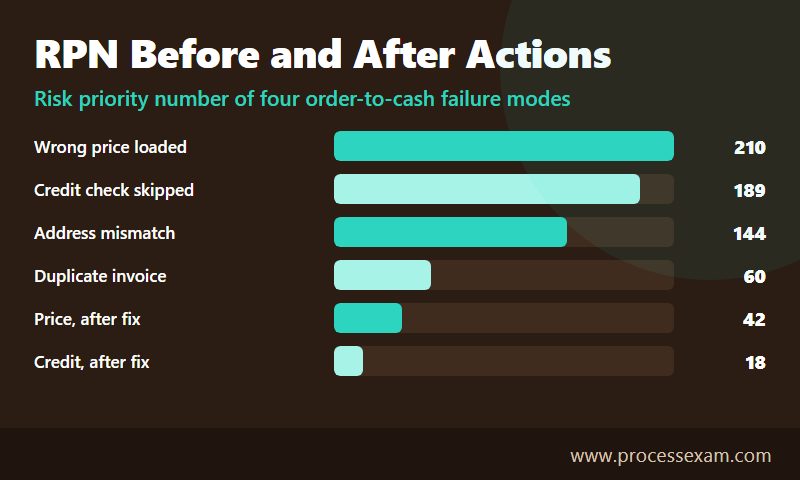
The four rows add up to an RPN of 603. A plain top-down ranking would start with the pricing error, but the skipped credit check deserves attention for a second reason: its severity is 9, so the severity rule applies even though its RPN sits second. The team assigns an owner and a date to both.
The recommended actions then target the two factors a team can actually move. For pricing, the price list is locked to the contract record, which cuts occurrence from 5 to 2, and a reviewer sees any manual price change, which improves detection from 6 to 3. For the credit check, the order system blocks release above a set value until credit approves, so occurrence drops from 3 to 1 and detection from 7 to 2.
Re-scoring after the actions gives 42 for pricing (7 x 2 x 3) and 18 for the credit check (9 x 1 x 2). The four rows now total 264 instead of 603, a fall of about 56 percent. Notice that severity did not change: the consequence of a wrong price is the same as before. Risk reduction in an FMEA almost always comes from occurrence and detection, which is why mistake-proofing is so popular.
Who should be in the room?
Scores are only as honest as the people giving them. A good FMEA team includes the person who does the work, someone who sees the downstream effect, a process owner and, where the data allows, someone who can pull defect history. Scores agreed by a manager alone tend to cluster around 5, and the ranking loses its value.
Where does risk show up in each DMAIC phase?
Each of the five DMAIC phases has a specific risk question to answer, and each leaves a document behind that someone can audit later.
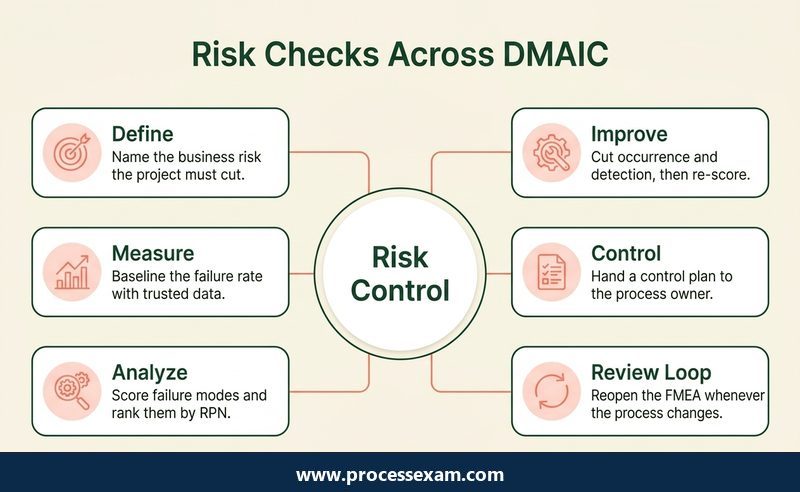
| Phase | Risk question | Typical tool | What you leave behind |
|---|---|---|---|
| Define | What could stop this project, and what could the process do to the customer? | Charter risk log, SIPOC, voice of the customer | Scoped risks and a signed charter |
| Measure | How often does the process fail today, and can we trust the data? | Measurement system analysis, DPMO, process capability | A baseline failure rate |
| Analyze | Which failure modes matter most, and what causes them? | FMEA, Pareto chart, fault tree, cause-and-effect diagram | A ranked list of failure modes |
| Improve | Does the fix cut the risk without creating a new one? | Pilot, mistake-proofing, re-scored FMEA | A lower RPN and a pilot result |
| Control | How will we notice the risk coming back? | Control plan, control charts, reaction plan | A handover to the process owner |
What does Define contribute?
Risk enters the project before any data does. The charter should state the business risk the project is meant to reduce, in the same unit the sponsor already tracks: warranty cost, regulatory findings, late shipments or rework hours. A team that cannot name the risk in a sponsor's terms usually ends up optimising something nobody asked for.
What does Measure contribute?
A risk score built on bad data is a confident guess. Before the baseline is accepted, a measurement system analysis checks that two people measuring the same item reach the same answer. Only then does the DPMO or capability index mean what it appears to mean, and only then can Improve claim a before-and-after difference.
What does Improve contribute?
The improvement phase is where a new risk can slip in. A faster approval step may reduce waiting but remove the one check that caught errors. Re-scoring the FMEA with the proposed solution in place, before the pilot starts, is the cheapest way to catch a fix that moves the risk rather than removing it.
What belongs in a control plan?
If the FMEA says where the risk lives, the control plan says who watches it and what happens when it moves. It is the document the project team hands to the process owner so that the gain survives the team's departure. One row of a useful control plan holds:
- the process step and the failure mode it addresses, copied from the FMEA so the two stay linked;
- the characteristic being controlled and its specification limits;
- the measurement method, the sample size and how often to sample;
- the control method, such as a control chart, a poka-yoke device or a mandatory system block;
- the reaction plan, meaning who stops the line or escalates, and in what time, when a signal appears.
Control charts are the signature Six Sigma control. They separate ordinary variation from a signal that something has changed, so the owner reacts to the second and leaves the first alone. A process whose long-term capability index (Cpk) is 1.33 or higher is conventionally treated as comfortably inside its limits, though the right target depends on what a miss costs.
Why are some controls better than others?
Controls are not equal. A system block that makes the failure impossible is stronger than an inspection that might catch it, and an inspection is stronger than a reminder in a procedure. When you re-score detection after an improvement, the rank of the control should drive the number. A step that now relies on a person remembering a rule should not drop to a detection score of 2.
How often should the FMEA itself be revisited?
The FMEA is a living document. Reopen it when the process changes, when a new failure turns up that nobody listed, when a customer complaint reveals an effect worse than scored, and on a fixed review date. A control plan with no review date tends to become a filing-cabinet item within a year.
How do you prove that the risk went down?
The claim "we reduced risk" needs the same evidence as any other Six Sigma claim: a baseline, a result, and a reason to believe the difference is real. Several measures work together.
- Total and top-item RPN. The example above went from 603 to 264. Report the top items too, because one severe failure mode can hide inside a falling total.
- DPMO or sigma level. If the order process produced 17 errors across 4,000 invoices with five error opportunities each, that is 20,000 opportunities and a DPMO of 850, or roughly a 4.6 sigma process. If a later sample shows 5 errors, the DPMO is 250, close to 5.0 sigma.
- Cost of poor quality. Translate defects into rework, credits, penalties and write-offs, so finance can see the saving.
- Leading and lagging indicators. A lagging indicator such as customer complaints confirms the result after the event. A leading indicator such as the share of orders needing a manual price override warns that the risk is returning before a complaint arrives.
Use a hypothesis test or a control chart over enough points to show that the drop is not a lucky month. A before-and-after pair of numbers from a single week proves very little, and a sceptical sponsor will say so.
How do you report it to leadership?
Keep the report short and in the sponsor's units: the risk named in the charter, the baseline, the new figure, the money involved and who now owns the control plan. A single page with the FMEA before and after and one chart of the key measure is usually enough for a risk committee.
When is Six Sigma the wrong tool for a risk?
Six Sigma suits risks that occur repeatedly and leave data behind. It is a poor fit when the event is rare, catastrophic or driven by outside forces. A once-in-a-decade supplier collapse, a regulatory change or a market shock has no process to measure and no defect rate to improve.
- Too little data. If there is no history, severity and occurrence scores are guesses, and the RPN presents the guess with false precision.
- External or strategic risk. Scenario planning, insurance, diversification and contingency plans are the stronger answers.
- Human and cultural risk. Conduct, ethics and culture are shaped by leadership behaviour. Six Sigma change management tools help, but a control chart will not fix them.
- Safety-critical designs. Methods built for hazards, such as a hazard analysis or fault tree, usually sit beside the FMEA rather than inside it.
The sensible position is to treat Six Sigma as one part of a wider risk framework. It handles operational risks that live inside repeatable processes, and the rest of the framework handles the others.
How does the ASQ Black Belt exam test this?
Risk is a named topic on the ASQ Certified Six Sigma Black Belt (CSSBB) exam. In ASQ's Body of Knowledge, "Risk Analysis and Management" sits inside the Analyze area. It covers the types of risk (enterprise, operational, supplier, security, product and cyber-security) and FMEA, including the RPN, the difference between DFMEA and PFMEA, and how to evaluate the results for processes, products and services. Control plans then appear in the Control area, which sets out how to maintain gains and hand over to the process owner. The CSSBB syllabus lists the full wording for each area.
| Item | CSSBB detail |
|---|---|
| Certification | ASQ Certified Six Sigma Black Belt (CSSBB) |
| Exam fee | ASQ MEMBERS - $485 NON-MEMBERS - $585 RETAKES - $385 |
| Questions | 165 |
| Duration | Total appointment time - 270 Exam time - 258 |
| Passing score | 550/750 |
| Areas with direct risk content | Analyze (22 questions) and Control (17 questions) |
ASQ's own page describes a one-part computer-based exam in which 150 questions are scored and 15 are unscored, and it requires three years of paid work in the Body of Knowledge areas plus one or two completed projects with signed affidavits. Check the ASQ Black Belt certification page for the current rules and testing windows.
What does an FMEA question look like?
Expect a small table of failure modes with S, O and D scores and a request to say which to address first, or what the RPN becomes after a described action. The trap is the one from the worked example: an answer ranked by RPN alone may ignore a high-severity item. Practise the arithmetic until it is automatic, because the exam is open book but 165 questions leave little room for slow sums.
Working through the CSSBB practice exam is a direct way to meet FMEA, RPN and control-plan questions in the wording ASQ uses, with the reasoning for each answer.
How much of this should you learn?
Know the three scales and the RPN formula, the DFMEA and PFMEA difference, why detection scores run backwards, how a control plan links to the FMEA, and how to read a control chart. That set covers the exam's treatment of risk without turning a topic article into a course.
Frequently Asked Questions
What is FMEA in Six Sigma?
Failure mode and effects analysis is a structured way to list how a process or design can fail, what the effect would be and why it happens. Each failure mode is scored for severity, occurrence and detection, and the three scores are multiplied into a risk priority number used to rank which failures to fix first.
How is the RPN calculated?
The risk priority number is severity multiplied by occurrence multiplied by detection, each scored from 1 to 10, giving a result between 1 and 1,000. A higher RPN means a higher priority. Detection runs backwards, so a score of 10 means the failure would almost certainly reach the customer undetected.
Does Six Sigma replace a risk register?
No. A risk register records and tracks risks across the organisation, while Six Sigma supplies measurement and improvement tools for risks that live in repeatable processes. In practice the FMEA output feeds the register, and the control plan shows who monitors each item afterwards.
Which DMAIC phase is FMEA used in?
Most teams build the FMEA in the Analyze phase to rank failure modes and causes, then re-score it in Improve to confirm the fix lowered the risk. The control plan in the Control phase carries the surviving high-priority items forward, and the FMEA is reopened whenever the process changes.
Is FMEA on the Six Sigma Black Belt exam?
Yes. ASQ's Certified Six Sigma Black Belt Body of Knowledge includes risk analysis and management, covering types of risk, FMEA, the RPN, and the difference between design and process FMEA. Control plans are tested separately in the Control area. The exam has 165 questions and a passing score of 550/750.
- Six Sigma |
- ASQ Six Sigma Black Belt Sample Questions |
- ASQ Six Sigma Black Belt Test Questions |
- CSSBB Question Bank |
- CSSBB Exam Questions Download |
- CSSBB Test Questions |
- Six Sigma Black Belt PDF |
- ASQ Six Sigma Black Belt Book |
- ASQ CSSBB BOK PDF |
- Six Sigma Black Belt Certification Cost |
- Six Sigma Black Belt Certification Requirements |
- CSSBB Body of Knowledge (BOK) |
- CSSBB Handbook


